HOW DRU CATCH SEES IT
The Most Ambitious "Clerical Error" in Dubai's Recent Legal History
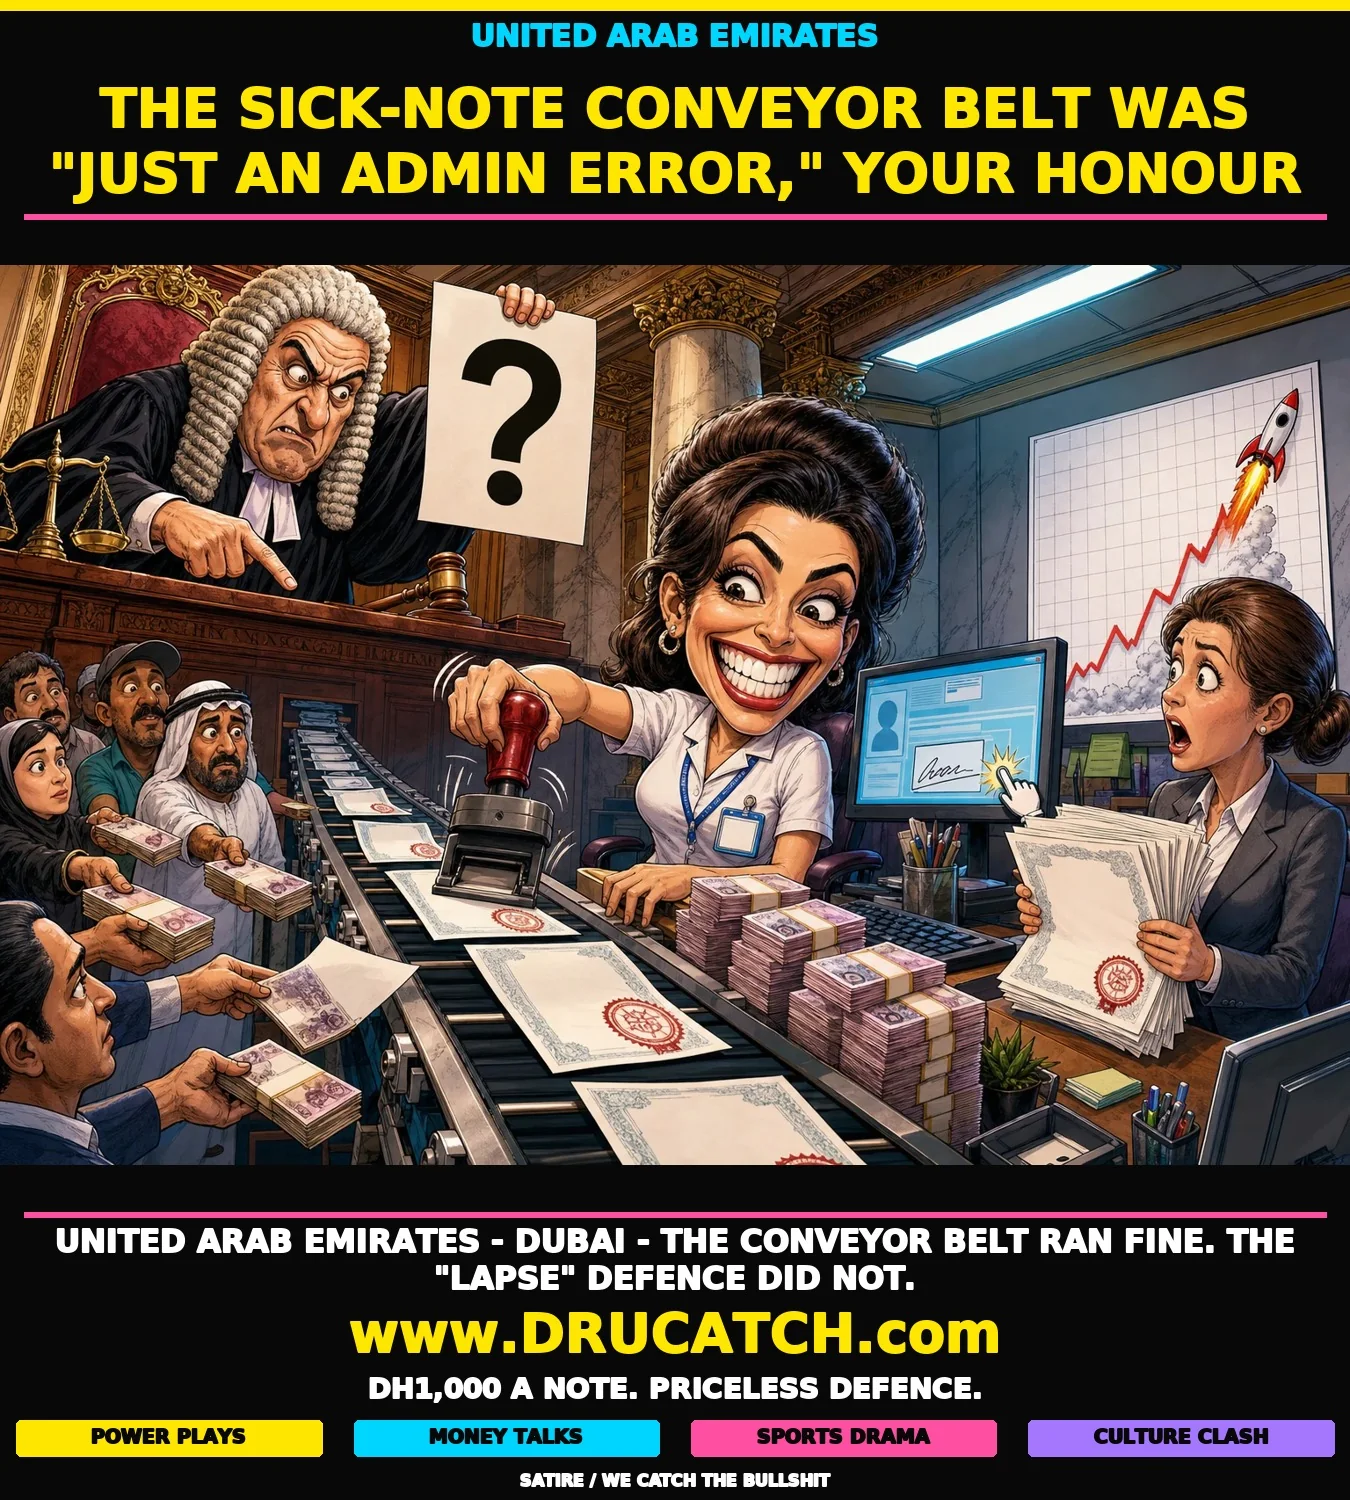
Calling a systematic, cash-rewarded certificate operation an "administrative lapse" takes a particular kind of nerve. A counterfeiter who borrows the treasury's own press and then describes the output as a printing accident is working from the same playbook. Administrative lapses are things like misfiled invoices or a missed approval step - not a recurring, fee-per-transaction arrangement that required actively navigating a clinic's digital health portal, backdating documents and applying forged doctor signatures on demand.
The Dubai Criminal Court was unmoved, ruling that the defendants had deliberately falsified official medical records and purposefully exploited the clinic's own electronic infrastructure. The defence, in other words, attempted the same move twice: first the scheme itself, then a courtroom retelling of it as an accident. The first attempt ran until an HR department noticed the pattern. The second attempt did not survive the judge's eyebrow.
Follow the thread: Iran Shuts the Oil Chokepoint "For the People" - While $110 Oil Crushes Them.
Why the Digital Health System Was the Point, Not Just the Tool
The scheme's real raw material wasn't the certificates - it was the institutional credibility baked into them. These weren't blurry photocopies passed under a table. Each document carried a legitimate digital stamp from an active clinic portal, with fabricated signatures attached to real doctors' identities. Dubai Police investigators found the clerk had used that portal to backdate records and push them through a system employers were entitled to trust. The very architecture of digital health verification - designed to protect workers - became the mechanism for billing their employers for days off that never had a medical basis.
That structural irony is also what makes the "unauthorised employee action" spin so strained. To accept it, a court would have had to conclude that someone stumbled, repeatedly and profitably, onto the precise sequence of steps needed to generate, backdate, and officially validate medical records - and that the cash changing hands each time was coincidental. Payments reportedly reached over Dh1,000 per certificate, according to the case as reported. Accidents rarely come with a price list.
The Employers Left Holding the Invoice for Every "Certified" Absence
Private companies absorbed the cost of every absence the certificates laundered into legitimacy. They paid full salaries for medically unverified leave, received no reimbursement when the fraud surfaced and had to rely on an internal HR review to catch what the system itself never flagged. It was the pattern - multiple absences, all stamped by the same clinic - that eventually tripped the alarm, not any built-in safeguard. The institutional faith placed in a certified digital health credential is exactly proportional to the damage one insider with portal access can quietly cause.
The court imposed prison terms, financial penalties and restitution, and directed that expatriate defendants be deported on completing their sentences. That closes the case. The open question it leaves behind - how a single clerk with no doctor present could operate a paid absence service through a system treated as legal proof of illness - is an architectural problem that no conviction, however satisfying, resolves on its own.
THE COMMENTS SECTION HAS ENTERED THE CHAT
Should digital health systems used for issuing workplace medical certificates require a second-level verification step - such as a doctor's direct confirmation - before a certificate becomes valid, to prevent insider exploitation of the kind seen in this Dubai case?
Join the discussion / save / share